Security expert warns JPMorgan Chase vendor breach could fuel phishing scams
Chase vendor hack could fuel wave of phishing scams, expert warns
newsnationnow.com· 39h
JPMorgan Chase Customer Data Is Exposed in Latest Hack
nytimes.com· 2d
A cyberattack leaks thousands of Chase customer emails and some phone numbers
apnews.com· 2d
Hackers leak customer data from JPMorgan Chase, Visa and Mastercard, Wall Street Journal reports
youtube.com· 2d
Cyberattack may have exposed Chase Bank and Mastercard customer data
washingtonpost.com· 2d
JPMorgan Chase customer emails, names may have been accessed in third-party hack
politico.com· 2d
JPMorgan Chase reveals data breach, but says it’s unrelated to this week’s banking outage
theverge.com· 2d
JPMorgan Chase says some customer data may be exposed after its vendors were hit by a cyberattack
businessinsider.com· 2d
Chase issues warning to customers of data breach
Hackers breached a vendor serving JPMorgan Chase, Visa and Mastercard, exposing names, email addresses and some phone numbers of customers.
Chase says the exposed data was marketing data held by vendors and included no credit card or particularly sensitive personal information.
Chase declined a ransom demand and notified White House officials overnight, according to two anonymous sources.
Chase says the breach is unrelated to an online banking outage earlier the same week, which it blamed on a software bug.
Affected customers are to be contacted and offered complimentary credit monitoring, and a security expert warns of phishing attempts to follow.
JPMorgan Chase said in a post on X on 19 November 2026 that third parties providing services to the firm were targeted in a cyberattack that accessed marketing data held by the vendors, possibly including customer names and email addresses.
JPMorgan Chase said the hack had no connection to the service disruption its customers experienced on Monday.
JPMorgan Chase said impacted customers would be contacted directly and offered complimentary credit monitoring.
JPMorgan Chase said impacted customers would be contacted directly and offered complimentary credit monitoring.
JPMorgan Chase said the hack had no connection to the service disruption its customers experienced on Monday.
It was not clear which vendors were targeted or how many JPMorgan Chase customers might be affected.
A report from Cybernews said a ransomware group leaked email addresses of about 16,000 JPMorgan Chase customers, a dataset apparently linked to the bank's invitation-only Reserve program.
Mastercard said an incident at a third-party provider exposed a limited amount of email addresses of a small subset of customers enrolled in a specific program.
A ransomware group was reported to have leaked customer data from Visa, Mastercard and JPMorgan Chase.
Personal information of thousands of JPMorgan Chase customers, mostly email addresses and in some cases phone numbers, was leaked onto the internet on 19 November 2026, with some bank employees' details also involved.
Mastercard spokesman Seth Eisen said the exposure had been contained and Mastercard's teams were working with the provider to support impacted cardholders as needed.
JPMorgan Chase declined a ransom demand from the hackers and notified White House officials of the breach overnight, according to two people familiar with the matter who spoke on condition of anonymity.
JPMorgan Chase, Visa and Mastercard said on 19 November 2026 that hackers stole names, email addresses and phone numbers belonging to some of their customers by breaching a vendor that worked for them.
The companies said no payments data such as card numbers was affected in the theft.
Chase attributed the online banking disruption some customers experienced earlier that week to a software bug.
A JPMorgan Chase spokesman said "the attackers accessed certain marketing data held by vendors that was limited to some customer names, email addresses and a small amount of other public information."
Visa blamed "a third-party service provider in Asia Pacific" and said "no payments data such as card numbers were affected."
Mastercard said the incident exposed "non-payments information" affecting a "small subset of cardholders."
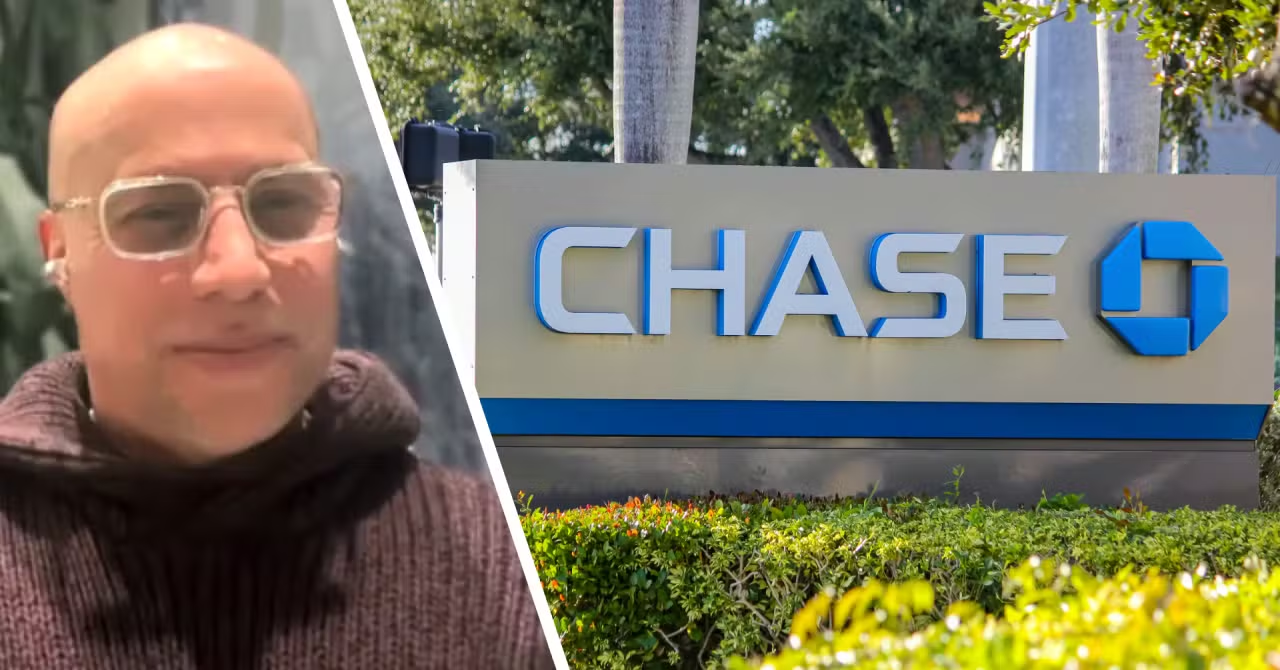
Security officer George Gerchow warned on 20 November 2026 that the breach of JPMorgan Chase vendors could fuel a wave of phishing attempts built on the exposed names and email addresses, including AI scams hard to spot.
George Gerchow, chief security officer at Bedrock Data, forecast a plethora of phishing attempts built on the exposed names and email addresses, including AI scams that will be hard to spot.
Gerchow called the Chase data breach "pretty harmful" and advised worried customers to stay calm and alert rather than panic, saying panic is exactly what the attackers want.